Cloud API authentication flow for unauthenticated callers
The following diagram identifies the flow of authentication and authorization information for unauthenticated callers. Colors are used in the following ways:
- Orange - credentials information
- Blue - endpoint access information
- Green - resource access information
- Red - proxy user and session user information
Some values are used to determine multiple types of access. These values initially appear as black (when they do not apply to a single type of access), and then later appear in one or more specific colors (to reflect the value is being used at that point in the process for a specific type of access).
In the following example, an API call is triggered by an unauthenticated caller.
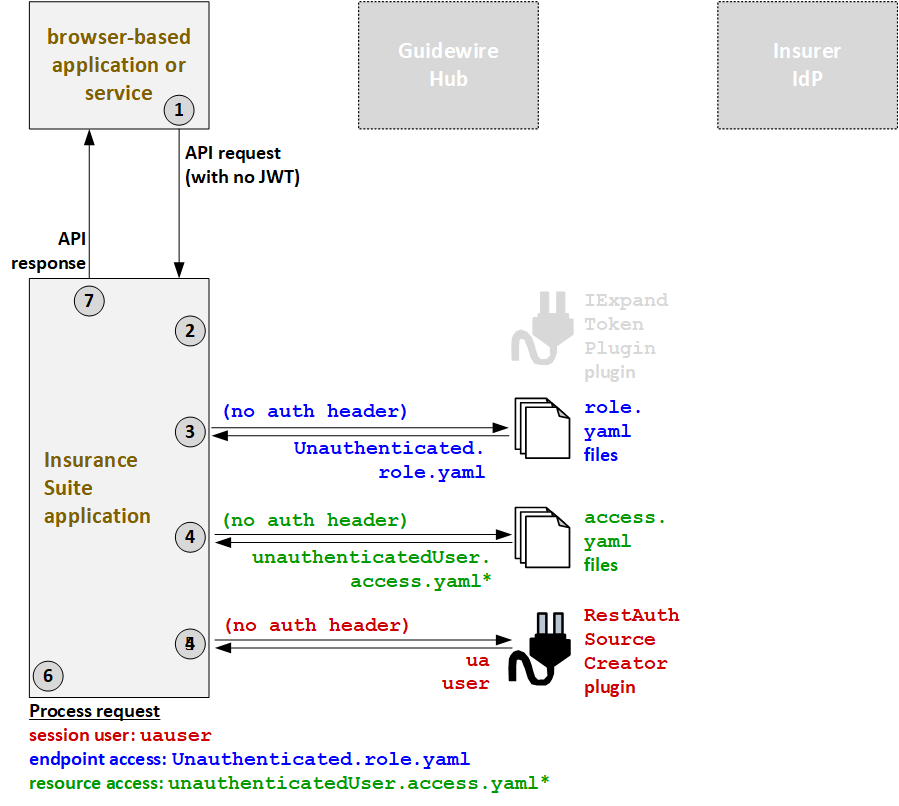
- The caller application sends the API request to the InsuranceSuite application. The call includes no JWT, and no authentication information in the header.
- The IExpandTokenPlugin plugin is not relevant for unauthenticated callers.
- Because the call has no authentication header, the InsuranceSuite application grants
endpoint access as defined in the
Unauthenticated.role.yamlAPI role file. (This provides access to metadata endpoints only.)Note: When PolicyCenter grants endpoint access as defined in theUnauthenticated.role.yamlAPI role file, this provides access to metadata endpoints as well as endpoints that can be used to create a new account. This is part of the anonymous auth flow. This only applies to PolicyCenter. - Because the call has no authentication header, InsuranceSuite application grants resource
access as defined in the
unauthenticatedUser.access.yamlAPI role file. (This provides no access to business resources.) - To determine which proxy user to assign to the session, the InsuranceSuite application
calls the
RestAuthenticationSourceCreatorplugin. The call has no authentication header. So, the plugin returns the proxy user for unauthenticated users:uauser. - The InsuranceSuite application processes the request.
- The session user is the proxy unauthenticated user:
uauser. - The endpoint access is defined by
Unauthenticated.role.yaml. - The resource access is defined by
unauthenticatedUseraccess.yaml.
- The session user is the proxy unauthenticated user:
- The InsuranceSuite application provides the response to the initial call.